


PCNSC Dumps By Pros - 1st Attempt Guaranteed Success
100% Guarantee Download PCNSC Exam Dumps PDF Q&A
NEW QUESTION 32
The firewall identified a popular application as a unknown-tcp. Which options are available to identify the application? (Choose two.)
- A. Create a customer object for the customer application server to identify the custom application.
- B. Create a custom application.
- C. Submit an App-ID request to Palo Alto Networks.
- D. Create a Security policy to identify the customer application.
Answer: A,B
NEW QUESTION 33
If an administrator wants to decrypt SMTP traffic and possesses the saver's certificate, which SSL decryption mode will allow the Palo Alto Networks NGFW to inspect traffic to the server?
- A. TLS Bidirectional Inspection
- B. SSL Inbound Inspection
- C. SSH Forward now proxy
- D. SMTP inbound Decryption
Answer: C
NEW QUESTION 34
A client has a sensitive application server in their data center and is particularly concerned about resource exhaustion because of distributed denial-of-service attacks.
How can the Palo Alto Networks NGFW be configured to specifically protect tins server against resource exhaustion originating from multiple IP address (DDoS attack)?
- A. Define a custom App-ID to ensure that only legitimate application traffic reaches the server
- B. Add a Vulnerability Protection Profile to block the attack.
- C. Add a DoS Protection Profile with defined session count.
- D. Add QoS Profiles to throttle incoming requests.
Answer: C
NEW QUESTION 35
What are two benefits of nested device groups in panorama? (Choose two )
- A. all device groups inherit setting from the Shared group
- B. reuse of the existing Security policy rules and objects
- C. requires configuration both function and location for every device
- D. overwrites local firewall configuration
Answer: A,C
NEW QUESTION 36
An administrator has users accessing network resources through Citrix XenApp 7 .x. Which User-ID mapping solution will map multiple mat who using Citrix to connect to the network and access resources?
- A. Client Probing
- B. Syslog Monitoring
- C. Terminal Services agent
- D. Globa1Protect
Answer: C
NEW QUESTION 37
Which two benefits come from assigning a Decrypting Profile to a Decryption rule with a" NO Decrypt" action? (Choose two.)
- A. Block sessions with client authentication
- B. Block sessions with untrusted issuers
- C. Block sessions with unsuspected cipher suites
- D. Block credential phishing.
- E. Block sessions with expired certificates
Answer: B,E
NEW QUESTION 38
Which Captive Portal mode must be contoured to support MFA authentication?
- A. NTLM
- B. Single Sign-On
- C. Redirect
- D. Transparent
Answer: C
NEW QUESTION 39
In High Availability, which information is transferred via the HA data link?
- A. heartbeats
- B. session information
- C. User-ID information
- D. HA state information
Answer: B
NEW QUESTION 40
Which feature prevents the submission of corporate login information into website forms?
- A. file blocking
- B. User-ID
- C. data filtering
- D. credential submission prevention
Answer: D
NEW QUESTION 41
Which three options are supposed in HA Lite? (Choose three.)
- A. active/passive deployment
- B. Virtual link
- C. session synchronization
- D. synchronization of IPsec security associations
- E. Configuration synchronization
Answer: A,D,E
NEW QUESTION 42
Refer to the exhibit.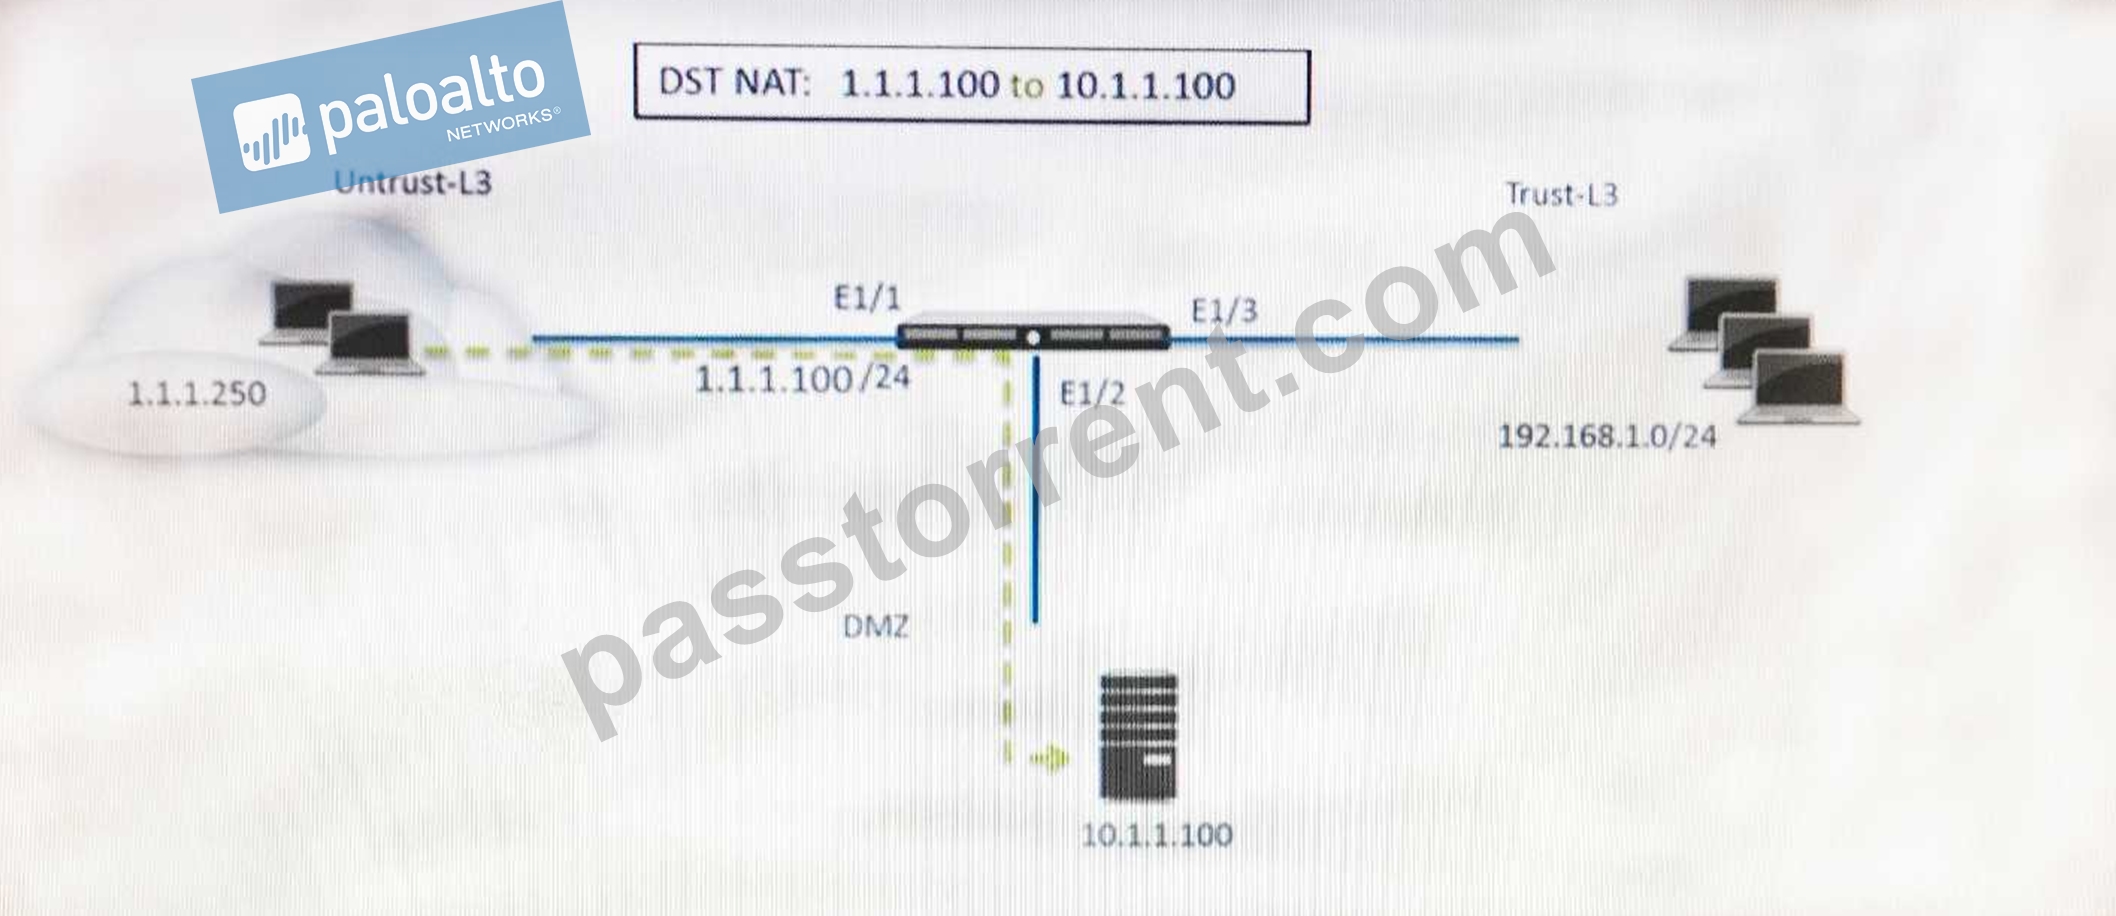
A web server in the DMZ is being mapped to a public address through DNAT.
Which Security policy rule will allow traffic to flow to the web server?
- A. Untrust (any) to Untrust (10. 1.1. 100), web browsing - Allow
- B. Untrust (any) to Untrust (1. 1. 1. 100), web browsing - Allow
- C. Untrust (any) to DMZ (10. 1. 1. 100), web browsing - Allow
- D. Untrust (any) to DMZ (1. 1. 1. 100), web browsing - Allow
Answer: B
NEW QUESTION 43
Which prerequisite must be satisfied before creating an SSH proxy Decryption policy?
- A. Both SSH keys and SSL certificates must be generated
- B. SSH keys must be manually generated
- C. SSL certificates must be generated
- D. No prerequisites are required
Answer: D
NEW QUESTION 44
A Company needs to preconfigured firewalls to be sent to remote sites with the least amount of preconfiguration. Once deployed, each firewall must establish secure tunnels back to multiple regional data centers to include the future regional data centers.
Which VPN configuration would adapt to changes when deployed to Hie future site?
- A. preconfigured PPTP Tunnels
- B. preconfigured iPsec tunnels
- C. preconfigured GlobalProtcet satellite
- D. preconfigured GlobalProtcet client
Answer: C
NEW QUESTION 45
A global corporate office has a large-scale network with only one User-ID agent, which creates a bottleneck near the User-ID agent server. Which solution in PAN -OS software would help in this case?
- A. redistribution of user mappings
- B. Virtual Wire mode
- C. application override
- D. content inspection
Answer: A
NEW QUESTION 46
Which PAN-OS policy must you configure to force a user to provide additional credential before he is allowed to access an internal application that contains highly sensitive business data?
- A. Decryption policy
- B. Application Override policy
- C. Authentication policy
- D. Security policy
Answer: C
NEW QUESTION 47
An administrator pushes a new configuration from panorama to a pair of firewalls that are configured as active/passive HA pair.
Which NGFW receives the configuration from panorama?
- A. both the active and passive firewalls independently, with no synchronization afterward
- B. the passive firewall, which then synchronizes to the active firewall
- C. the active firewall, which then synchronizes to the passive firewall
- D. both the active and passive firewalls, which then synchronizes with each other
Answer: D
NEW QUESTION 48
Which two action would be part of an automatic solution that would block sites with untrusted certificates without enabling SSL forward proxy? (Choose two.)
- A. Create a Security Policy rule with vulnerability Security Profile attached.
- B. Configure an EDL to pull IP Addresses of known sites resolved from a CRL.
- C. Configure a Dynamic Address Group for untrusted sites.
- D. Create a no-decrypt Decryption Policy rule.
- E. Enable the "Block seasons with untrusted Issuers- setting.
Answer: A,E
NEW QUESTION 49
What is exchanged through the HA2 link?
- A. HA state information
- B. User-ID in information
- C. session synchronization
- D. hello heartbeats
Answer: C
NEW QUESTION 50
Which event will happen administrator uses an Application Override Policy?
- A. The Palo Alto Networks NGFW Steps App-ID processing at Layer 4.
- B. Threat-ID processing time is decreased.
- C. The application name assigned to the traffic by the security rule is written to the traffic log.
- D. App-ID processing time is increased.
Answer: A
NEW QUESTION 51
An administrator has been asked to configure active/passive HA for a pair of Palo Alto Networks NGFWs.
The administrator assigns priority 100 to the active firewall.
Which priority is collect tot the passive firewall?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
NEW QUESTION 52
During the packet flow process, which two processes are performed in application identification? (Choose two.)
- A. pattern based application identification
- B. application override policy match
- C. session application identified
- D. Application changed from content inspection
Answer: B,C
NEW QUESTION 53
......
Earn Quick And Easy Success With PCNSC Dumps: https://www.passtorrent.com/PCNSC-latest-torrent.html
Kickstart your Career with Real Updated Questions: https://drive.google.com/open?id=1LT3MD_tt9GA26kD90AsPd46FrB2kQ7AC