


[Full-Version] 2026 New PassTorrent SC-100 PDF Recently Updated Questions
SC-100 Exam with Guarantee Updated 298 Questions
NEW QUESTION # 75
Case Study 2 - Litware, inc.
Overview
Litware, Inc. is a financial services company that has main offices in New York and San Francisco. Litware has 30 branch offices and remote employees across the United States. The remote employees connect to the main offices by using a VPN.
Litware has grown significantly during the last two years due to mergers and acquisitions. The acquisitions include several companies based in France.
Existing Environment
Litware has a Microsoft Entra tenant that syncs with an Active Directory Domain Services (AD DS) forest named litware.com and is linked to 20 Azure subscriptions. Microsoft Entra Connect is used to implement pass-through authentication. Password hash synchronization is disabled, and password writeback is enabled. All Litware users have Microsoft 365 E5 licenses.
The environment also includes several AD DS forests, Microsoft Entra tenants, and hundreds of Azure subscriptions that belong to the subsidiaries of Litware.
Requirements. Planned Changes
Litware plans to implement the following changes:
- Create a management group hierarchy for each Microsoft Entra tenant.
- Design a landing zone strategy to refactor the existing Azure environment of Litware and deploy all future Azure workloads.
- Implement Microsoft Entra Application Proxy to provide secure access to internal applications that are currently accessed by using the VPN.
Requirements. Business Requirements
Litware identifies the following business requirements:
- Minimize any additional on-premises infrastructure.
- Minimize the operational costs associated with administrative overhead.
Requirements. Hybrid Requirements
Litware identifies the following hybrid cloud requirements:
- Enable the management of on-premises resources from Azure, including the following:
o Use Azure Policy for enforcement and compliance evaluation.
o Provide change tracking and asset inventory.
o Implement patch management.
- Provide centralized, cross-tenant subscription management without the overhead of maintaining guest accounts.
Requirements. Microsoft Sentinel Requirements
Litware plans to leverage the security information and event management (SIEM) and security orchestration automated response (SOAR) capabilities of Microsoft Sentinel. The company wants to centralize Security Operations Center (SOC) by using Microsoft Sentinel.
Requirements. Identity Requirements
Litware identifies the following identity requirements:
- Detect brute force attacks that directly target AD DS user accounts.
- Implement leaked credential detection in the Microsoft Entra tenant of Litware.
- Prevent AD DS user accounts from being locked out by brute force attacks that target Microsoft Entra user accounts.
- Implement delegated management of users and groups in the Microsoft Entra tenant of Litware, including support for:
o The management of group properties, membership, and licensing
o The management of user properties, passwords, and licensing
o The delegation of user management based on business units
Requirements. Regulatory Compliance Requirements
Litware identifies the following regulatory compliance requirements:
- Ensure data residency compliance when collecting logs, telemetry, and data owned by each United States- and France-based subsidiary.
- Leverage built-in Azure Policy definitions to evaluate regulatory compliance across the entire managed environment.
- Use the principle of least privilege.
Requirements. Azure Landing Zone Requirements
Litware identifies the following landing zone requirements:
- Route all internet-bound traffic from landing zones through Azure Firewall in a dedicated Azure subscription.
- Provide a secure score scoped to the landing zone.
- Ensure that the Azure virtual machines in each landing zone communicate with Azure App Service web apps in the same zone over the Microsoft backbone network, rather than over public endpoints.
- Minimize the possibility of data exfiltration.
- Maximize network bandwidth.
The landing zone architecture will include the dedicated subscription, which will serve as the hub for internet and hybrid connectivity. Each landing zone will have the following characteristics:
- Be created in a dedicated subscription.
- Use a DNS namespace of litware.com.
Requirements. Application Security Requirements
Litware identifies the following application security requirements:
- Identify internal applications that will support single sign-on (SSO) by using Microsoft Entra Application Proxy.
- Monitor and control access to Microsoft SharePoint Online and Exchange Online data in real time.
To meet the application security requirements, which two authentication methods must the applications support? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Kerberos
- B. NTLMv2
- C. certificate-based authentication
- D. Security Assertion Markup Language (SAML)
Answer: A,D
Explanation:
Litware identifies the following application security requirements:
Identify internal applications that will support single sign-on (SSO) by using Microsoft Entra Application Proxy.
You can provide single sign-on (SSO) to on-premises applications that are secured with SAML authentication and provide remote access to these applications through Application Proxy. With SAML single sign-on, Microsoft Entra ID authenticates to the application by using the user's Microsoft Entra account.
You can provide single sign-on for on-premises applications published through Application Proxy that are secured with integrated Windows authentication.
These applications require a Kerberos ticket for access. Application Proxy uses Kerberos Constrained Delegation (KCD) to support these applications.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/app-proxy/application-proxy-configure-single-sign-on-on-premises-apps https://docs.microsoft.com/en-us/azure/active-directory/app- proxy/application-proxy-configure-single-sign-on-with-kcd
https://docs.microsoft.com/en-us/azure/active-directory/app-proxy/application-proxy-configure-custom-domain
NEW QUESTION # 76
You have an Azure SQL database named DB1 that contains customer information.
A team of database administrators has full access to DB1.
To address customer inquiries, operators in the customer service department use a custom web app named App1 to view the customer information.
You need to design a security strategy for D81. The solution must meet the following requirements:
* When the database administrators access DB1 by using SQL management tools, they must be prevented from viewing the content of the Credit Card attribute of each customer record.
* When the operators view customer records in App1, they must view only the last four digits of the Credit Card attribute.
What should you include in the design? To answer, select the appropriate options in the answer area. NOTE:
Each correct selection is worth one point.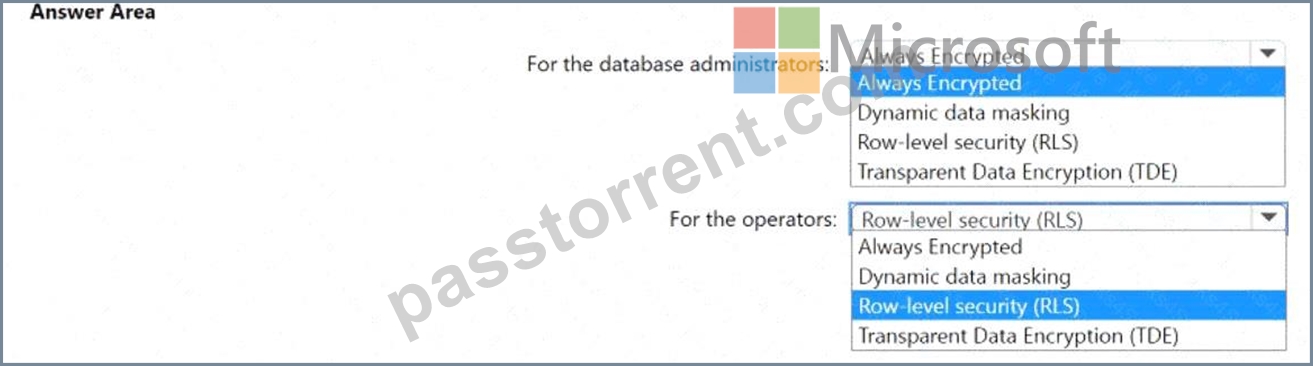
Answer:
Explanation: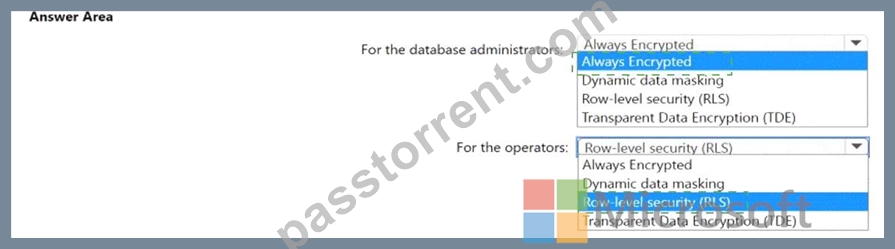
Explanation: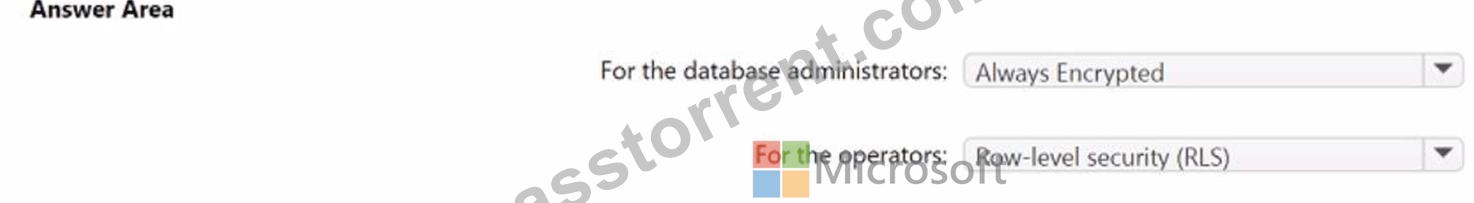
NEW QUESTION # 77
Your company is developing an invoicing application that will use Azure AD B2C. The application will be deployed as an App Service web app.
You need to recommend a solution to the application development team to secure the application from identity-related attacks.
Which two configurations should you recommend? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Azure AD Conditional Access integration with user flows and custom policies
- B. smart account lockout in Azure AD B2C
- C. custom resource owner password credentials (ROPC) flows in Azure AD B2C
- D. access packages in Identity Governance
Answer: A,B
Explanation:
Smart lockout is supported by user flows, custom policies, and ROPC flows. It's activated by default so you don't need to configure it in your user flows or custom policies.
NEW QUESTION # 78
You have a Microsoft 365 tenant that uses Microsoft SharePoint Online and Microsoft Purview.
Microsoft Purview has a sensitivity label named Label1 that is applied to the files stored on SharePoint Online sites.
You need to recommend a Microsoft Purview Data Loss Prevention (DLP) policy that meets the following requirements:
- Prevents users from uploading the files to third-party external
websites
- Allows users to upload the files to Microsoft OneDrive for Business
To which location should you apply the DLP policy?
- A. OneDrive accounts
- B. Devices
- C. SharePoint sites
- D. Microsoft Defender for Cloud Apps
Answer: B
Explanation:
To prevent users from uploading files with a specific sensitivity label (like Label1) to third-party external websites while allowing uploads to Microsoft OneDrive for Business, you would apply the Microsoft Purview Data Loss Prevention (DLP) policy to Devices. Applying the DLP policy to Devices allows control over what users do with files on their endpoints, enabling you to prevent data from being shared to untrusted locations while allowing uploads to trusted services such as OneDrive for Business.
NEW QUESTION # 79
Your on-premises network contains an Active Directory Domain Services (AD DS) domain named corpxontoso.com and an AD DS-integrated application named App1.
Your perimeter network contains a server named Server1 that runs Windows Server.
You have a Microsoft Entra tenant named contoso.com that syncs with corp.contoso.com.
You plan to implement a security solution that will include the following configurations:
* Manage access to App1 by using Microsoft Entra Private Access.
* Deploy a Microsoft Entra application proxy connector to Server1.
* Implement single sign-on (SSO) for App1 by using Kerberos constrained delegation.
* For Server1, configure the following rules in Windows Defender Firewall with Advanced Security:
o Rule1: Allow TCP 443 inbound from a designated set of Azure URLs.
o Rule2: Allow TCP 443 outbound to a designated set of Azure URLs.
o Rule3: Allow TCP 80 outbound to a designated set of Azure URLs.
o Rule4: Allow TCP 389 outbound to the domain controllers on corp.contoso.com.
You need to maximize security for the planned implementation. The solution must minimize the impact on the connector.
Which rule should you remove?
- A. Rule1
- B. Rule3
- C. Rule4
- D. Rule2
Answer: B
NEW QUESTION # 80
You have an Azure subscription that contains an Azure Synapse Analytics workspace named workspace1.
workspace1 contains a built-in serverless SQL pool and a dedicated SQL pool named Pool1.
You need to recommend a second layer of data encryption for workspace1.
What should you include in the recommendation for each pool? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.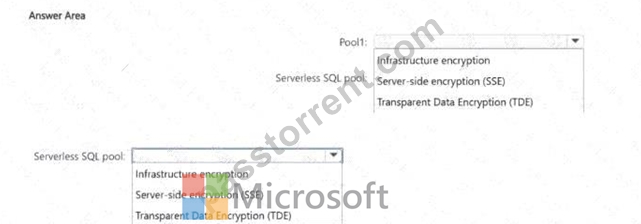
Answer:
Explanation: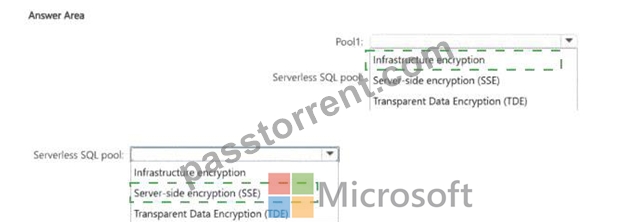
Explanation: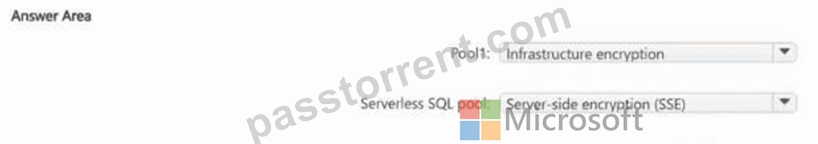
NEW QUESTION # 81
You are designing security for an Azure landing zone. Your company identifies the following compliance and privacy requirements:
* Encrypt cardholder data by using encryption keys managed by the company.
* Encrypt insurance claim files by using encryption keys hosted on-premises.
Which two configurations meet the compliance and privacy requirements? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Store the cardholder data in an Azure SQL database that is encrypted by using Microsoft-managed Keys.
- B. Store the insurance claim data in Azure Blob storage encrypted by using customer-provided keys.
- C. Store the cardholder data in an Azure SQL database that is encrypted by using keys stored in Azure Key Vault Managed HSM
- D. Store the insurance claim data in Azure Files encrypted by using Azure Key Vault Managed HSM.
Answer: B,D
Explanation:
https://azure.microsoft.com/en-us/blog/customer-provided-keys-with-azure-storage-service-encryption/
Topic 2, Fabrikam, Inc Case Study 1
OverView
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.
fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
* An Azure Active Directory (Azure AD) tenant named fabrikam.onmicrosoft.com that syncs with corp.
fabnkam.com
* A single Azure subscription named Sub1
* A virtual network named Vnet1 in the East US Azure region
* A virtual network named Vnet2 in the West Europe Azure region
* An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAR enabled
* A Microsoft Sentinel workspace
* An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
* 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
* A resource group named TestRG that is used for testing purposes only
* An Azure Virtual Desktop host pool that contains personal assigned session hosts All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure-.
* An Azure AD tenant named contoso.onmicrosoft.com
* An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications. The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1.
The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
* Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
* Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
* Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation-. Machines should have a vulnerability assessment solution.
All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
* ClaimsApp will be deployed to Azure App Service instances that connect to Vnetl and Vnet2.
* Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
* ClaimsApp will access data in ClaimsDB.
* ClaimsDB must be accessible only from Azure virtual networks.
* The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
* Azure DevTest labs will be used by developers for testing.
* All the application code must be stored in GitHub Enterprise.
* Azure Pipelines will be used to manage application deployments.
* All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
* Internet-accessible applications must prevent connections that originate in North Korea.
* Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
* Administrators must connect to a secure host to perform any remote administration of the virtual machines.
The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
* Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
* Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers;
* Every month, the membership of the ContosoDevelopers group must be verified.
* The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
* The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
NEW QUESTION # 82
You have an Azure subscription that contains 100 virtual machines. The virtual machines are accessed by using Azure Bastion.
You need to recommend a solution to ensure that only specific users in specific locations can access the virtual machines. The solution must meet the following requirements:
* Restrict access to the virtual machines based on an originating IP address or a connection request by using just-in-time (JIT) VM access network-based controls.
* Restrict access to the virtual machines based on role-based access control (RBAC) role assignments by using JIT VM access authorization controls.
Which Microsoft cloud services should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.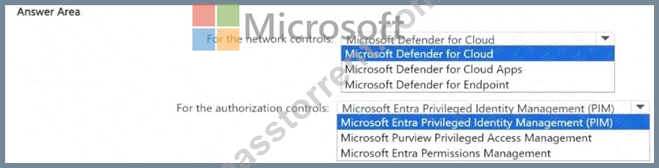
Answer:
Explanation: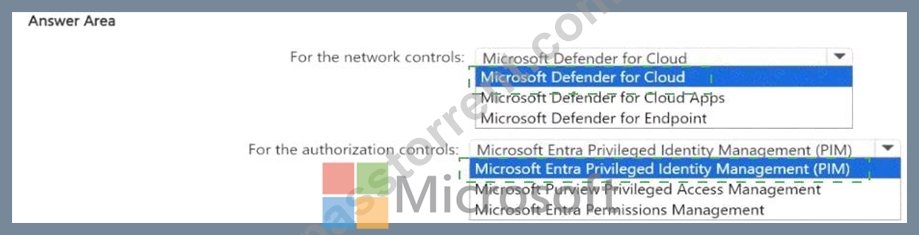
Explanation: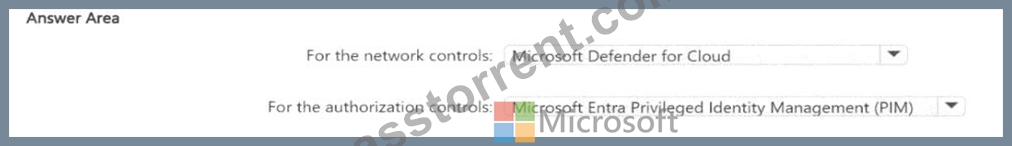
NEW QUESTION # 83
You have three Microsoft Entra tenants named Tenant 1. Tenant2. and Tenant3.
You have three Azure subscriptions named Sub1, Sub2, and Sub3. Each tenant is associated with multiple Azure subscriptions.
Each subscription contains a single Microsoft Sentinel workspace as shown in the following table.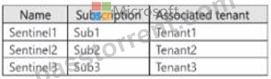
You need to recommend a solution that meets the following requirements:
* Ensures that the users in Tenant1 can manage the resources in Sub2 and Sub3 without having to switch subscriptions or sign in to a different tenant
* Implements multiple workspace view for Sentinel2 and Sentinel3
What should you use to delegate permissions, and which Microsoft Sentinel feature will users be able to manage in multiple workspace view? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.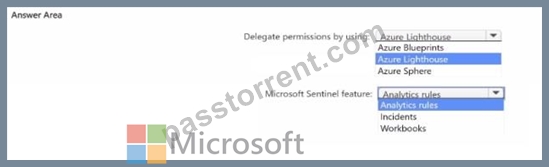
Answer:
Explanation: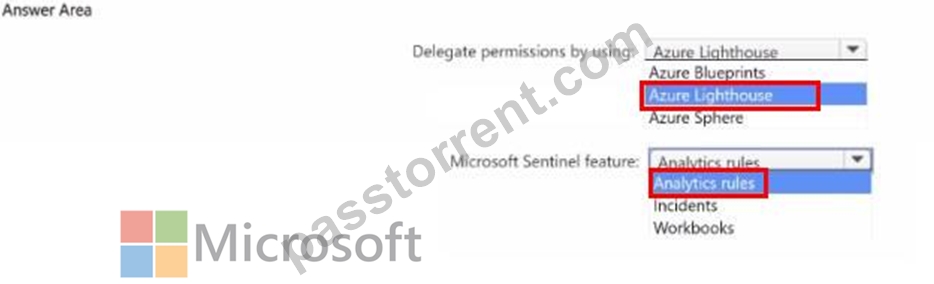
NEW QUESTION # 84
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.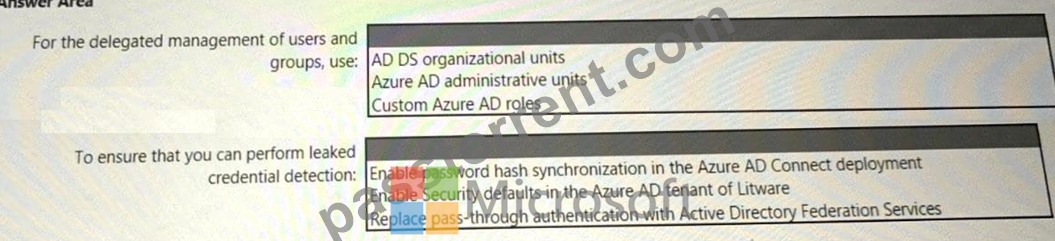
Answer:
Explanation: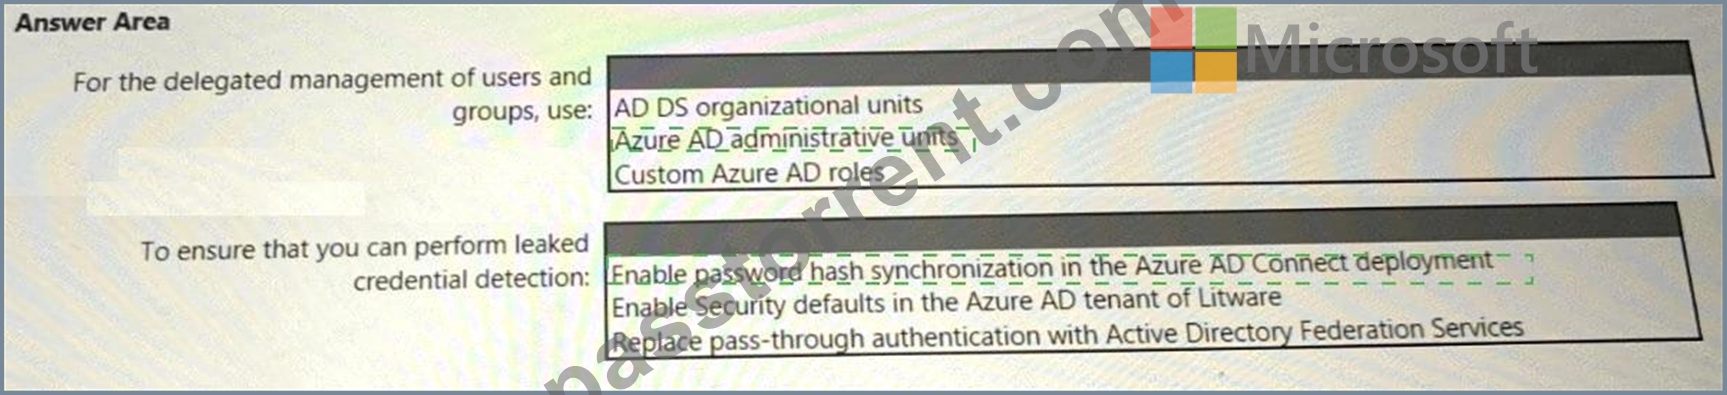
Explanation: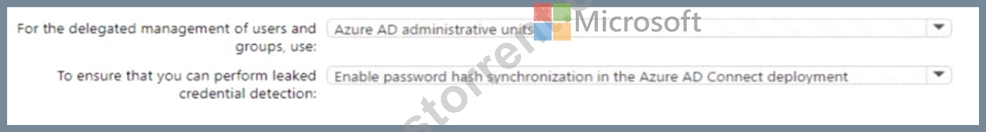
NEW QUESTION # 85
You have a Microsoft 365 subscription
You need to recommend a security solution to monitor the following activities:
* User accounts that were potentially compromised
* Users performing bulk file downloads from Microsoft SharePoint Online What should you include in the recommendation for each activity? To answer, drag the appropriate components to the correct activities. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each Correct selection is worth one Point.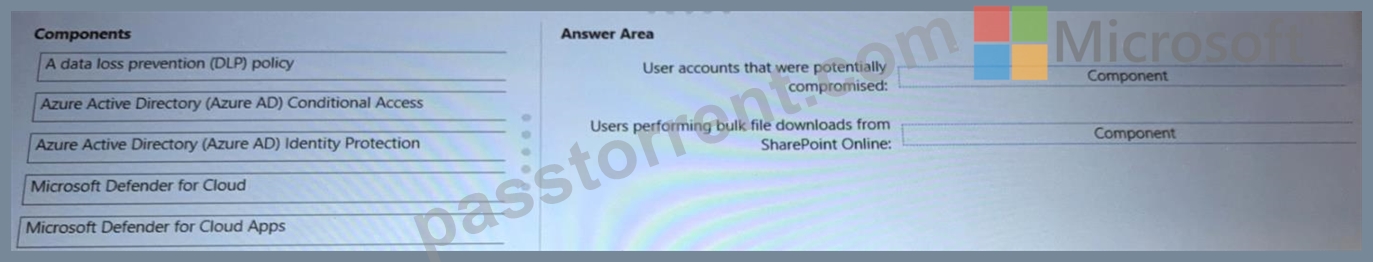
Answer:
Explanation: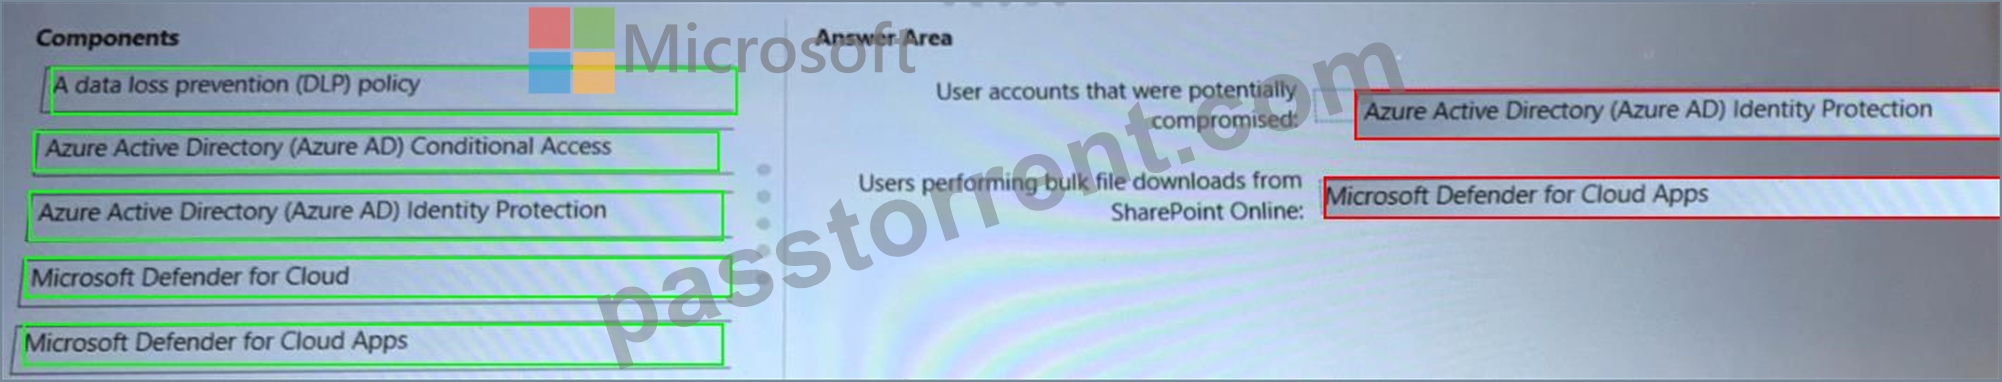
NEW QUESTION # 86
Your company has a multi-cloud environment that contains a Microsoft 365 subscription, an Azure subscription, and Amazon Web Services (AWS) implementation. You need to recommend a security posture management solution for the following components:
* Azure loT Edge devices
* AWS EC2 instances
Which services should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.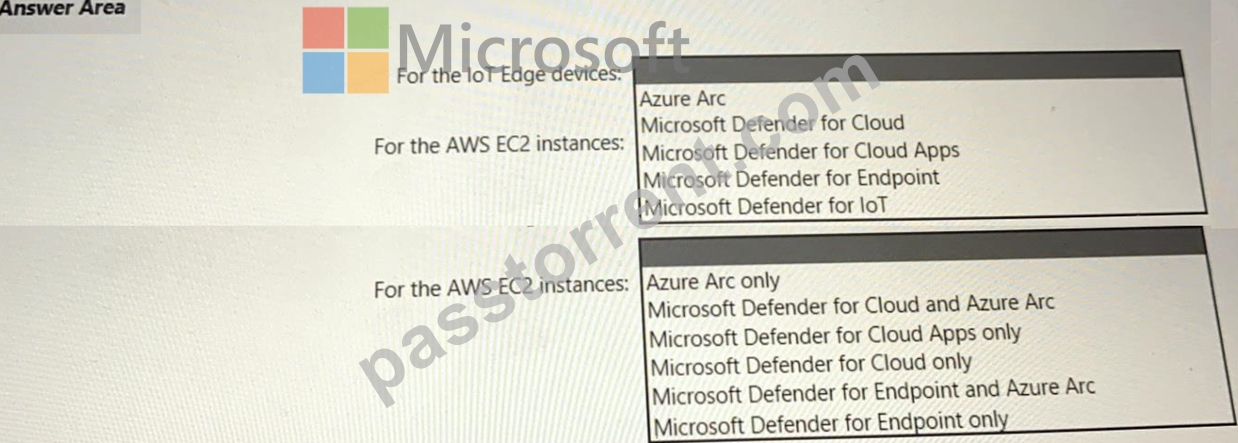
Answer:
Explanation: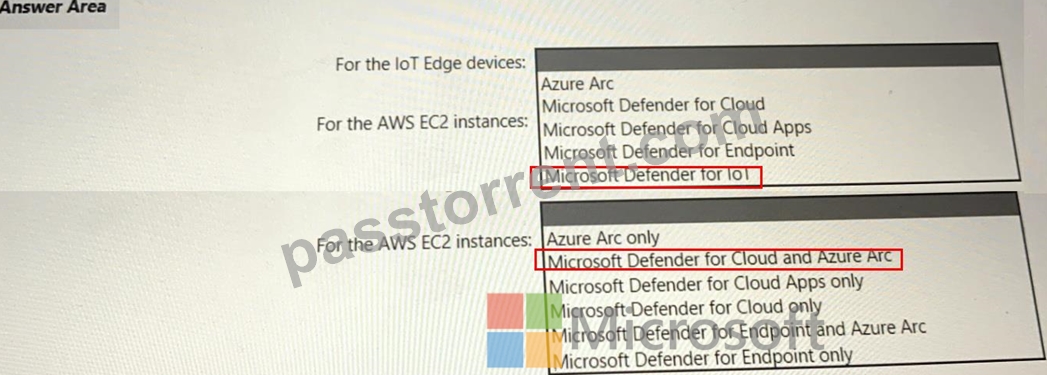
NEW QUESTION # 87
Your company plans to move all on-premises virtual machines to Azure. A network engineer proposes the Azure virtual network design shown in the following table.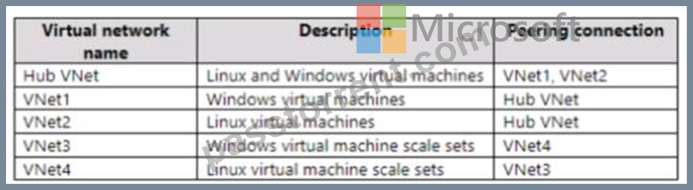
You need to recommend an Azure Bastion deployment to provide secure remote access to all the virtual machines. Based on the virtual network design, how many Azure Bastion subnets are required?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
Answer: A
Explanation:
https://docs.microsoft.com/en-us/azure/bastion/vnet-peering
https://docs.microsoft.com/en-us/learn/modules/connect-vm-with-azure-bastion/2-what-is-azure-bastion
NEW QUESTION # 88
Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.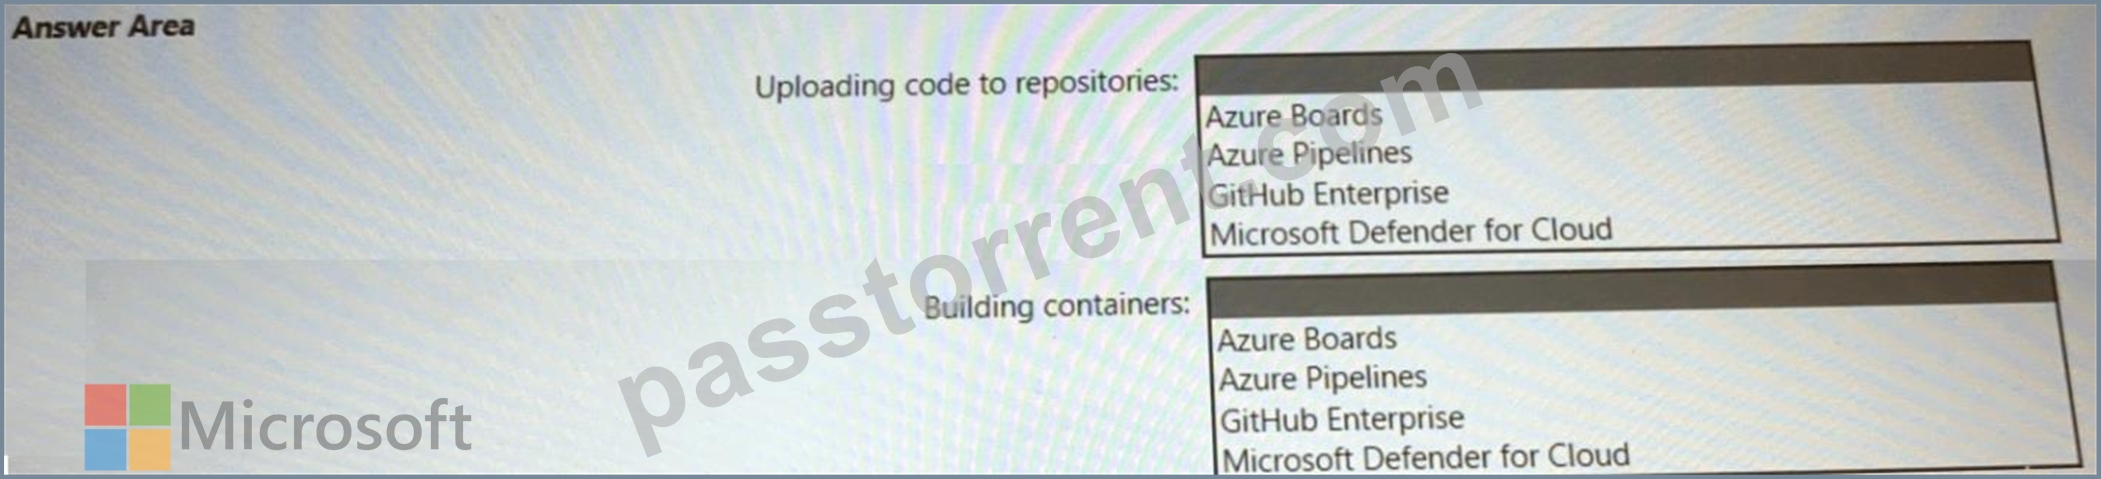
Answer:
Explanation: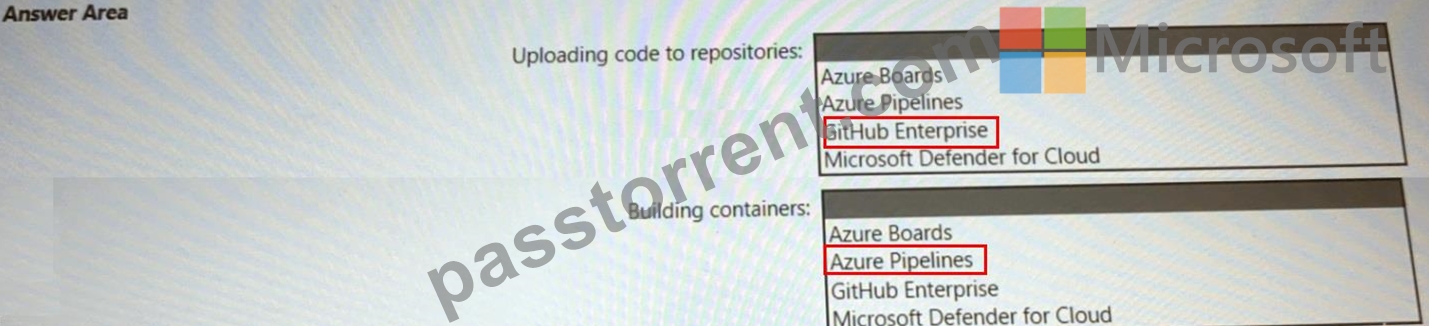
NEW QUESTION # 89
You have an Azure SQL database named DB1 that contains customer information.
A team of database administrators has full access to DB1.
To address customer inquiries, operators in the customer service department use a custom web app named App1 to view the customer information.
You need to design a security strategy for D81. The solution must meet the following requirements:
* When the database administrators access DB1 by using SQL management tools, they must be prevented from viewing the content of the Credit Card attribute of each customer record.
* When the operators view customer records in App1, they must view only the last four digits of the Credit Card attribute.
What should you include in the design? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.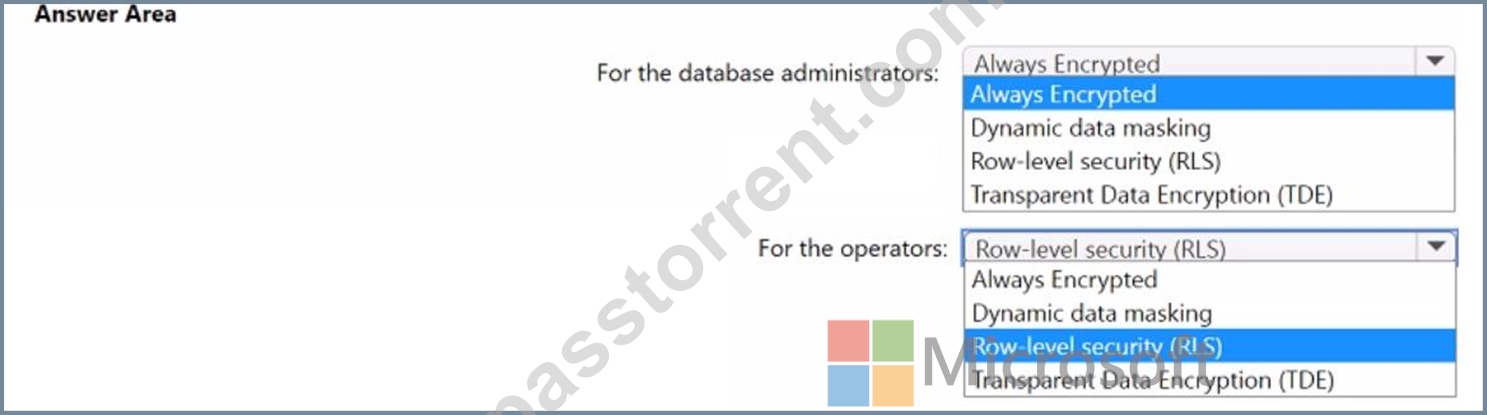
Answer:
Explanation: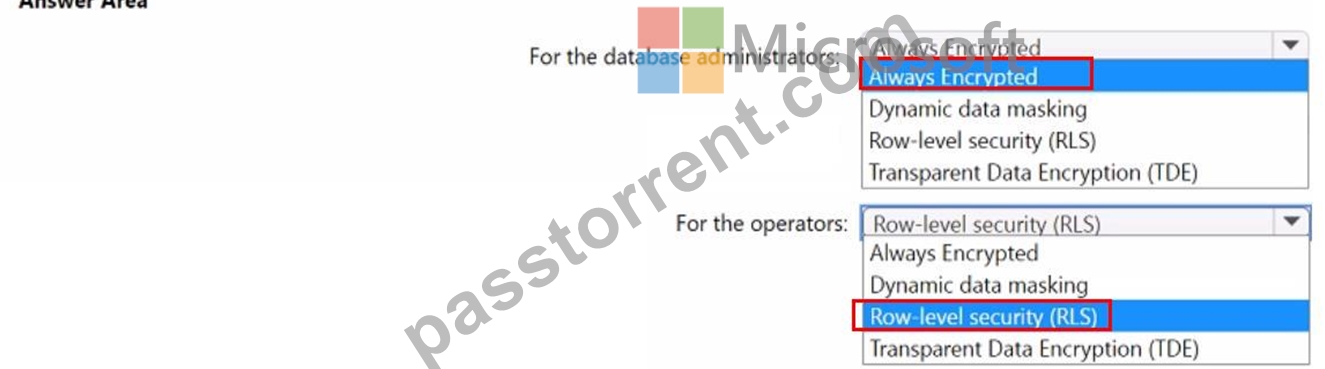
NEW QUESTION # 90
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.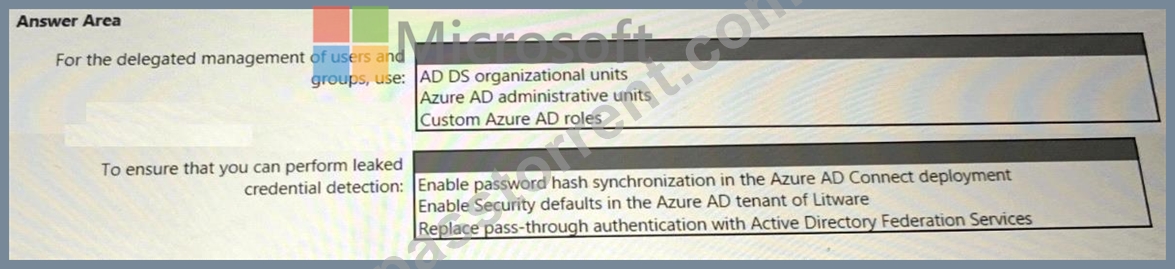
Answer:
Explanation: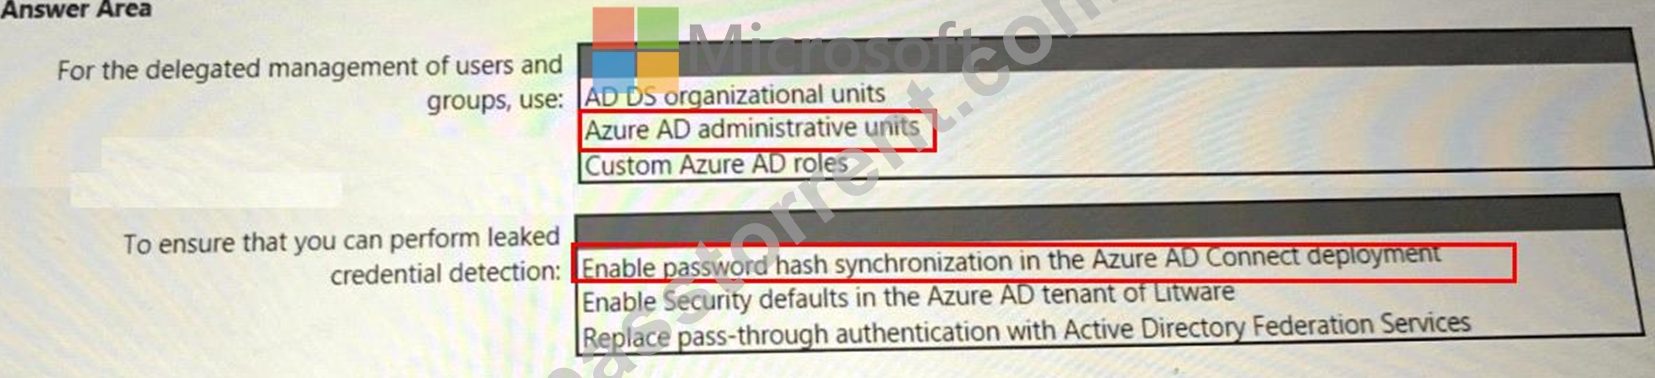
NEW QUESTION # 91
You have a Microsoft 365 subscription
You need to recommend a security solution to monitor the following activities:
* User accounts that were potentially compromised
* Users performing bulk file downloads from Microsoft SharePoint Online What should you include in the recommendation for each activity? To answer, drag the appropriate components to the correct activities. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each Correct selection is worth one Point.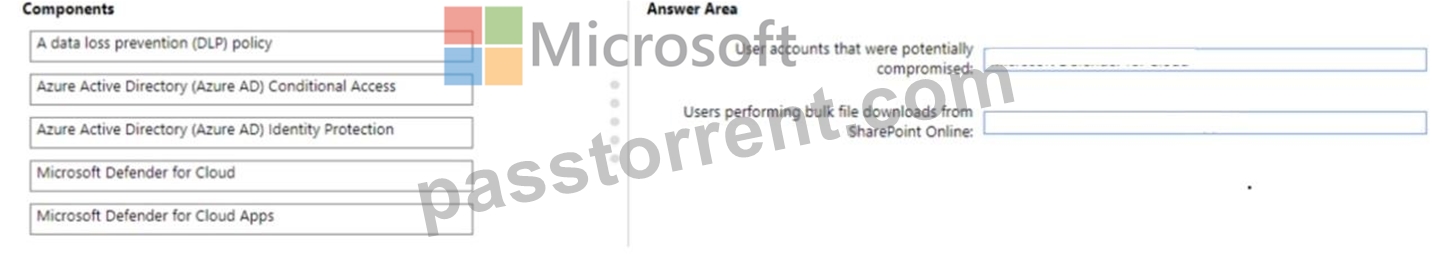
Answer:
Explanation: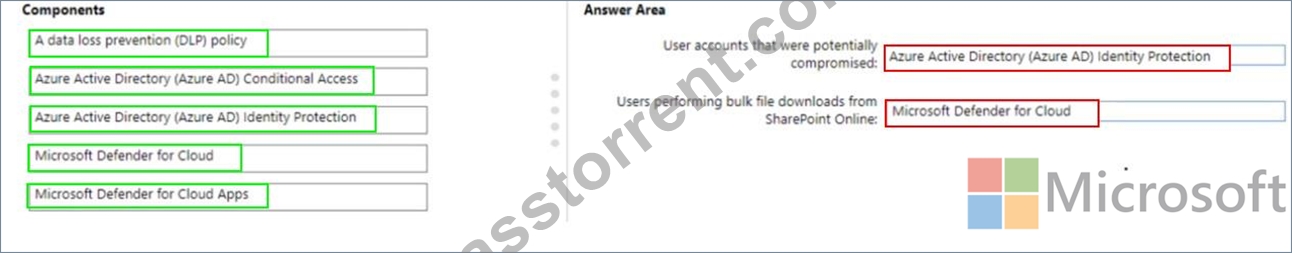
NEW QUESTION # 92
You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.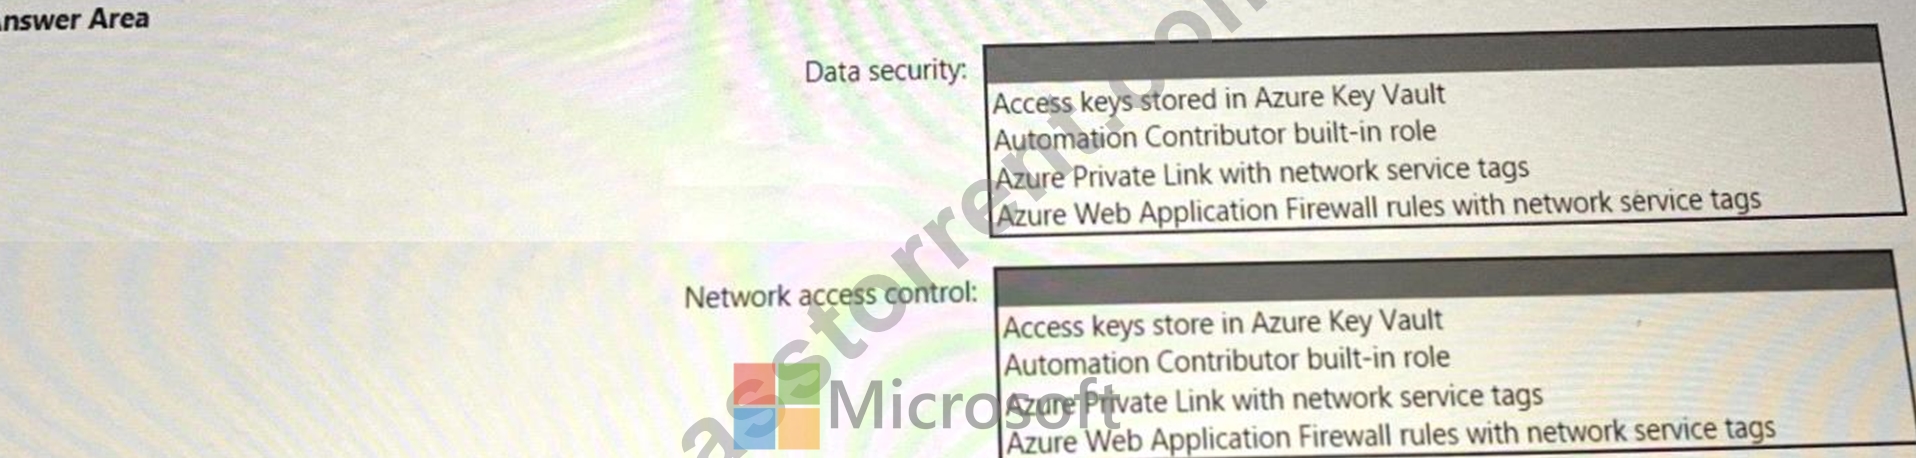
Answer:
Explanation: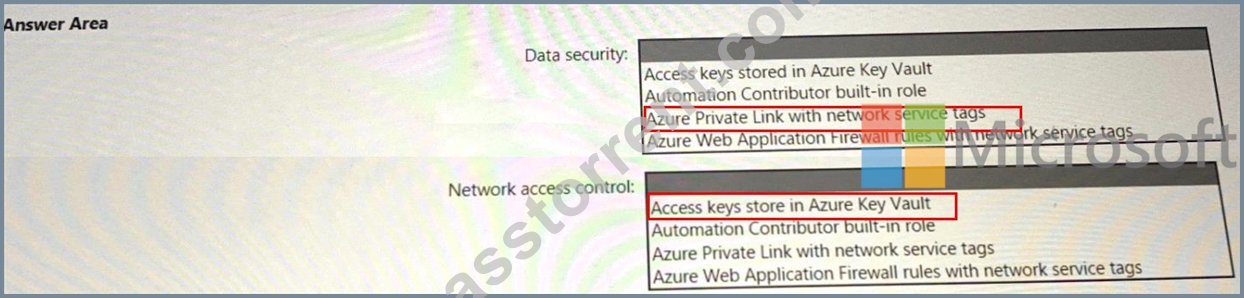
NEW QUESTION # 93
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains a Microsoft Sentinel workspace. Microsoft Sentinel data connectors are configured for Microsoft 365, Microsoft 365 Defender, Defender for Cloud, and Azure.
You plan to deploy Azure virtual machines that will run Windows Server.
You need to enable extended detection and response (EDR) and security orchestration, automation, and response (SOAR) capabilities for Microsoft Sentinel.
How should you recommend enabling each capability? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.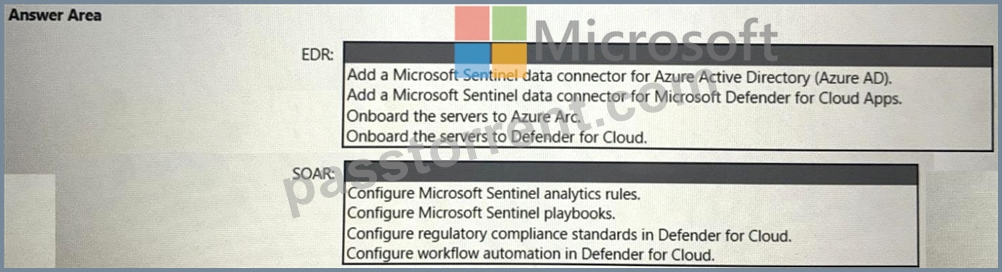
Answer:
Explanation: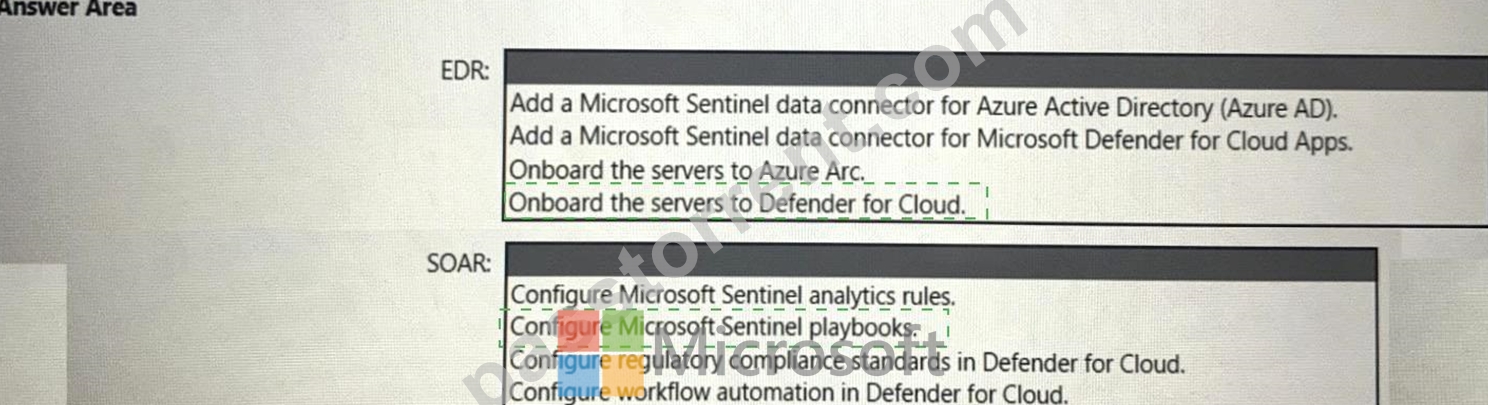
Explanation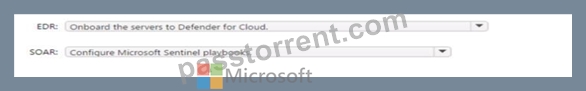
For SOAR read this https://docs.microsoft.com/en-us/azure/sentinel/automate-responses-with-playbooks Endpoint detection and response (EDR) and eXtended detection and response (XDR) are both part of Microsoft Defender.
https://docs.microsoft.com/en-us/microsoft-365/security/defender/eval-overview?view=o365-worldwide
NEW QUESTION # 94
......
Latest SC-100 Pass Guaranteed Exam Dumps Certification Sample Questions: https://www.passtorrent.com/SC-100-latest-torrent.html
SC-100 Updated Exam Dumps [2026] Practice Valid Exam Dumps Question: https://drive.google.com/open?id=1XphAQBK_mcsA-qjg3JZ7_Y5TzcSLCyGF